Akuity Platform Custom Roles
Custom roles add support for Role Based Access Control (RBAC) for resources in the Akuity Platform (e.g. an Instance, or an Organization). Users can create and attach custom roles to API Keys to limit their access.
note
Support for custom roles on organization members is coming soon.
Managing Custom Roles
Only users with the Owner role in an organization can manage custom roles. They are read-only for everyone else.
-
Select the Organization you want to create a role for, from the pull down menu.
-
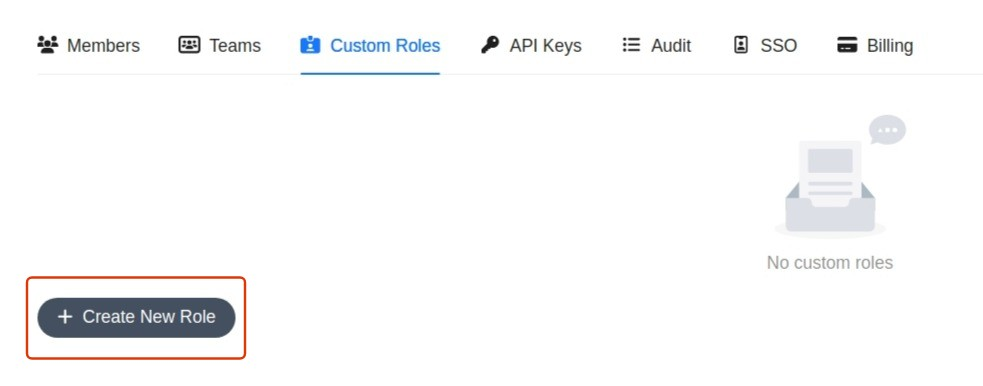
Switch to the Custom Roles tab.
-
Click on the "Create New Role" button to create a new role.
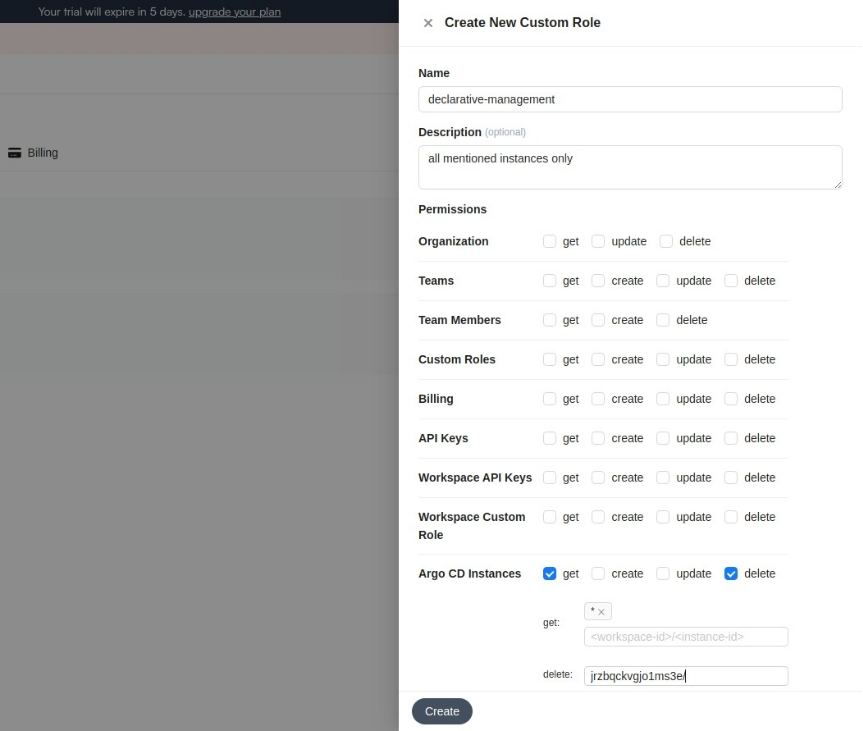
- Provide the name, description, and permissions of role. Then create the role. Please note that you can only add granular permissions for ArgoCD Instance, ArgoCD Cluster, Kargo Instance and Kargo Agent.
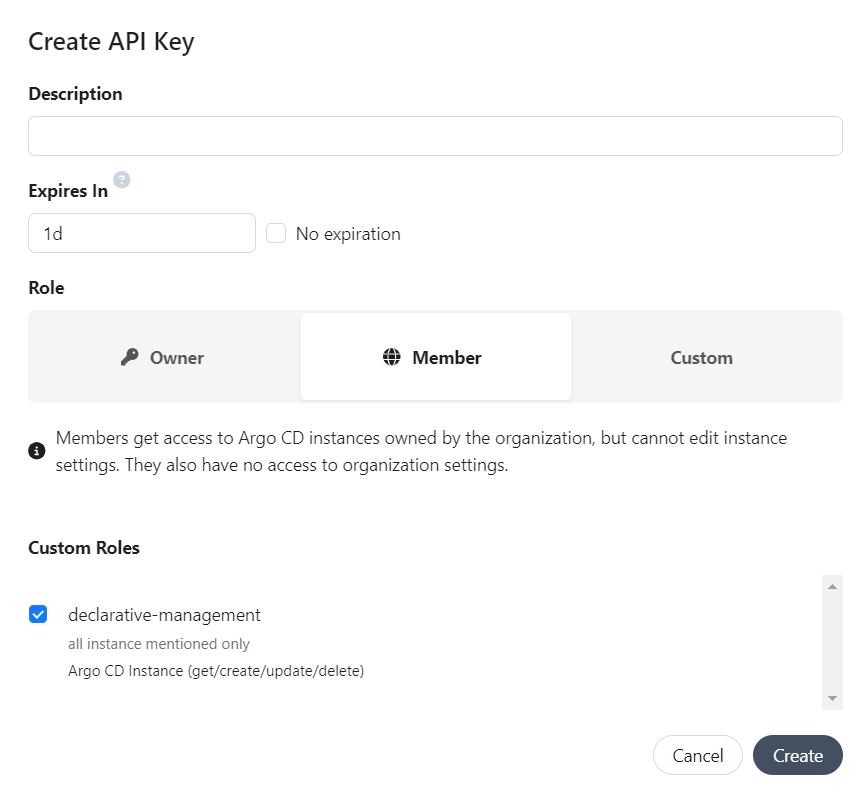
- You can then use that role when creating an API key.
Available permissions
Here is a table of current permissions which can be used in a custom role
| Resource | Get | Create | Update | Delete |
|---|---|---|---|---|
| Organization | ✅ | ❌ | ✅ | ✅ |
| Custom Roles | ✅ | ✅ | ✅ | ✅ |
| Billing | ✅ | ✅ | ✅ | ✅ |
| API Keys | ✅ | ✅ | ✅ | ✅ |
| Argo CD Instance | ✅ | ✅ | ✅ | ✅ |
| Argo CD Cluster | ✅ | ✅ | ✅ | ✅ |
| Kargo Instance | ✅ | ✅ | ✅ | ✅ |
| Kargo Agent | ✅ | ✅ | ✅ | ✅ |
| SSO Configuration | ✅ | ✅ | ✅ | ✅ |
| Member Role | ❌ | ❌ | ✅ | ❌ |
| Audit Log | ✅ | ❌ | ❌ | ❌ |
| OIDC Map | ✅ | ❌ | ✅ | ❌ |
| Notification Config | ✅ | ✅ | ✅ | ✅ |
| Teams | ✅ | ✅ | ✅ | ✅ |
| Team Members | ✅ | ✅ | ❌ | ✅ |
| Workspaces | ✅ | ✅ | ✅ | ✅ |
| Workspace Members | ✅ | ✅ | ❌ | ✅ |
| Workspace Member Role | ❌ | ❌ | ✅ | ❌ |
| Workspace API Keys | ✅ | ✅ | ✅ | ✅ |
| Workspace Custom Role | ✅ | ✅ | ✅ | ✅ |
| Kubernetes Dashboard | ✅ | ❌ | ❌ | ❌ |
| AI Agents | ✅ | ✅ | ✅ | ✅ |